60 Day Trial: IDE Integrated Agency Time Tracking, Privacy First

60 Day Trial: IDE Integrated Agency Time Tracking, Privacy First
IDE-integrated automatic tracking beats every manual alternative for agency time tracking because it logs billable coding hours the moment you write code, with no timer to start or timesheet to fill in later. JustClock does this across more than 20 IDEs, including JetBrains, VS Code, and Cursor, while keeping the tracking privacy-first, meaning it captures project and activity metadata, not your source code. If you bill clients by the hour, start the 60-day free trial and let a week of real project data settle the question.
TL;DR:
- IDE-native tracking provides minute-level, project-specific billing data by automatically logging activity during coding sessions across over 20 supported editors.
- Privacy-focused tools limit data collection to project metadata and activity timestamps, excluding source code content or keystrokes, with opt-in controls and data deletion options.
- To ensure billing accuracy, run a short pilot on complex projects with multiple branches, supplementing IDE tracking with separate logs for meetings and research activities.
- When selecting a tracker, verify comprehensive IDE support, clear data export options, robust admin controls, and strong security measures like encryption and access restriction.
- JustClock offers a 60-day free trial, supporting quick setup, detailed project mapping, and secure, privacy-respecting activity collection for agency billing workflows.
Table of Contents
- Why IDE-Integrated Automatic Tracking Wins for Dev Agencies
- What Should a Developer Time-Tracking Privacy Checklist Include?
- How Do You Choose an IDE Time Tracker for Agency Billing?
- Setting Up an Agency-Wide Time Tracking Workflow
- Why JustClock Fits This Job
- What Security Measures Protect Tracked Time Data?
- Start a Pilot With JustClock
- An Editorial Take on Adopting IDE-Integrated Tracking
- Sources
Why IDE-Integrated Automatic Tracking Wins for Dev Agencies
Manual timesheets fail for one simple reason: developers forget to start the timer. You get absorbed in a bug, lose forty minutes to a rabbit hole, and by the time you remember to log it, the memory of which project it belonged to has already faded. IDE-native tracking removes that failure point entirely by watching editor activity and attributing it to the project you’re actually working in, in real time.
This matters most at billing reconciliation. A plugin that maps active files to a project folder gives you a defensible, minute-level record instead of a guess reconstructed on Friday afternoon.
It also has real limits worth naming upfront. IDE-native tracking sees what happens inside the editor. It generally does not capture terminal sessions, browser research, client calls, or design tool work, so a complete billing picture still needs those pieces reconciled separately, a point Keito’s developer time-tracking guide makes explicitly when comparing tracking methods.
- Zero-friction capture: no start/stop button, no forgotten sessions
- Project-level attribution: time maps to the actual client codebase, not a guess
- Coverage gap: meetings, terminal use, and browser research fall outside editor tracking
- Responsible use: track work patterns, not individual performance scores
Pro Tip: Treat IDE-tracked data as a billing input, not a performance review. Using it to rank individual developers instead of validating invoices is a fast way to lose trust on your own team.
What Should a Developer Time-Tracking Privacy Checklist Include?
Any tool that watches your editor all day needs to earn trust on exactly what it collects, and the answer should be specific, not a vague privacy policy paragraph. Here’s what belongs on the “acceptable” side of the ledger and what should trigger a hard pass.
- Acceptable telemetry: project name, file type, active window duration, timestamp ranges.
- Unacceptable telemetry: source code content, keystrokes, clipboard contents, screenshots.
- Opt-in defaults: telemetry should require explicit enablement, not silent collection turned on by default.
- Admin controls: team leads should be able to see and adjust what’s collected across the organization, not just per user.
- Retention windows: ask how long raw activity data is stored before it’s aggregated or deleted.
- Export and deletion: confirm there’s an API or dashboard option to export your data and delete it on request.
JetBrains’ own product data collection notice is a useful reference point here. It documents that detailed code-related data can be collected under certain configurations, and that consent and admin controls determine what actually gets sent. That’s the standard to hold every vendor to, not just the one that happens to write it down clearly.
Research on developer tool privacy also recommends redaction at the edge rather than broad capture followed by filtering later. If a vendor can’t explain where redaction happens, in the plugin locally or somewhere on their servers, ask again before you sign anything.
How Do You Choose an IDE Time Tracker for Agency Billing?
Picking a tracker for client billing is a different exercise than picking one for personal curiosity. You need auditable, exportable, defensible numbers, and you need them fast enough to not slow down invoicing.
Run through this checklist before committing:
- IDE coverage: does it support every editor your team actually uses, including secondary tools like Android Studio or RustRover?
- Auto-capture fidelity: does it distinguish idle time from active coding, and does it track at minute-level granularity or something coarser?
- Project mapping: can you map folders or repos to specific clients without manual tagging every session?
- Data export: does it output CSV, API access, or a format your invoicing software can ingest directly?
- Admin controls: can a team lead configure telemetry settings and review usage across seats?
- Integration depth: does it connect to your existing billing or project management stack?
During a trial, ask the vendor directly: what exact fields does the plugin send home, can telemetry run fully disabled, and what happens to historical data if we cancel? The LIDE security research on coding agents lists exactly these questions, disabling telemetry and monitoring what extensions actually do, as the top mitigation strategies developers use against tool-based risk.
Red flags during a pilot include vague answers about data retention, no visible admin dashboard, or a plugin that requires broad filesystem permissions beyond the editor itself.
A realistic timeline: run a focused one to two week pilot across two or three developers first. Then use the 60-day trial window to validate billing accuracy against real invoices before rolling out to the whole team. ROI shows up fast here. Even a handful of previously unbilled hours per developer per month typically covers the subscription cost several times over.
Pro Tip: Run the pilot on your messiest project, not your cleanest one. If the tracker holds up on a codebase with five open branches and constant context-switching, it’ll hold up anywhere.
Setting Up an Agency-Wide Time Tracking Workflow
Rolling this out across a team goes smoother when you treat it as a short pilot with a review checkpoint, not a mandate handed down on day one.
- Install the plugin on two or three developer machines first, matching each person’s actual IDE.
- Map projects to client codebases so tracked time attributes correctly from day one.
- Run it for one to two weeks without changing anyone’s workflow.
- Review weekly, spending five minutes categorizing tracked blocks and flagging anything that looks off, a practice Keito’s guide specifically recommends for catching drift early.
- Scale to the full team once the numbers reconcile against actual invoices.
Reconciliation is the piece teams underestimate. Editor time won’t cover meetings, terminal debugging sessions, or browser-based research, so build a habit of logging those separately, even briefly, and add them to the same weekly review. For export, look for CSV or API output that flows into your invoicing tool, and consider linking reports to Git commit history for an extra layer of audit trail on disputed hours.
Why JustClock Fits This Job
JustClock was built around the exact workflow described above: install the plugin, keep coding, and let the billing data build itself.
- Automatic IDE plugins across more than 20 environments, including the JetBrains family, VS Code, and Devin
- activity capture mapped to individual client projects with fine time granularity
- Privacy-first collection limited to project, activity, and user metadata, never source code or keystrokes
- A 60-day free trial long enough to validate a full billing cycle before paying anything
IDE-specific setup docs exist for individual editors like WebStorm, RubyMine, and IntelliJ IDEA, and the JustClock blog covers deeper practitioner workflows and rollout stories for teams further along in adoption.
What Security Measures Protect Tracked Time Data?
Privacy controls tell you what’s collected. Security measures tell you what happens to that data once it exists, and the two get confused constantly in vendor marketing.
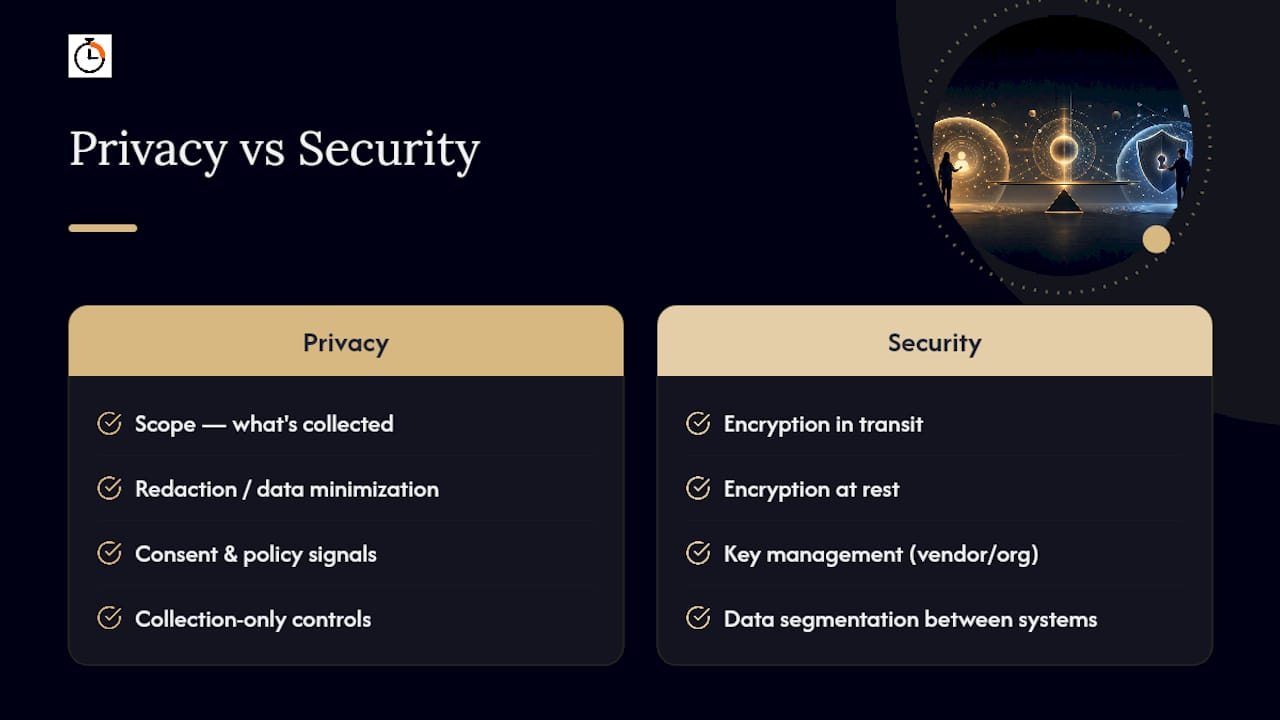
Encryption in transit and at rest is the baseline. Activity metadata should be encrypted moving from the plugin to any server, and encrypted again while stored, so a breach at the storage layer doesn’t expose raw usage logs. Ask specifically whether encryption keys are managed by the vendor or by your organization. Vendor-managed keys are simpler to set up. Organization-managed keys give you more control if you’re handling sensitive client relationships that require it.
Data segmentation matters just as much as encryption. Activity metadata, billing records, and account credentials should live in separated systems, not one database where a single compromised credential exposes everything. Ask whether the vendor runs regular third-party security audits or penetration tests, and whether results are shared, even in summary form, with customers.
Access control rounds this out. Who inside the vendor’s own organization can see raw activity logs, and is that access logged and limited by role? A vendor that can answer this in one sentence, versus one that redirects to a generic trust page, tells you a lot about how seriously security is actually handled internally.
None of this replaces the privacy checklist covered earlier. Encryption protects data that shouldn’t have been collected in the first place just as thoroughly as it protects data that should. Both layers need to hold up together.
Start a Pilot With JustClock
You’ve seen the checklist, the setup steps, and the security questions worth asking. The fastest way to know if IDE-integrated tracking actually fits your billing workflow is to run it against a real project for a short trial period, not read another comparison.
Head to the JustClock landing page to start the 60-day free trial, or jump straight to the setup page for your editor. VS Code users, JetBrains users, and Cursor users each get a dedicated install guide built for their environment. Install it on one or two machines, map your current client projects, and let it run untouched for about one to two weeks.
By the end of that window, you should have a clean, fine-grained record of coding time per project, ready to compare against what you actually invoiced last month. Just remember what the plugin won’t catch: client calls, terminal debugging, and browser research still need a separate note until you build the reconciliation habit into your weekly review. That gap closes fast once it’s part of the routine, and the 60-day window gives you room to prove the billing accuracy before any payment is due.
An Editorial Take on Adopting IDE-Integrated Tracking
The teams that get this right treat tracked data as a starting draft for the invoice, not the final word, and reconcile it weekly rather than at month end when memory has already faded. For workflows and rollout stories beyond this framework, the JustClock blog is worth a look.
— Rafal